How to Set Up a Virtual Network in LayerOne
Create a private network under Network, connect your servers, choose static addressing or DHCP, and keep public IPv4 off when a server should stay isolated.
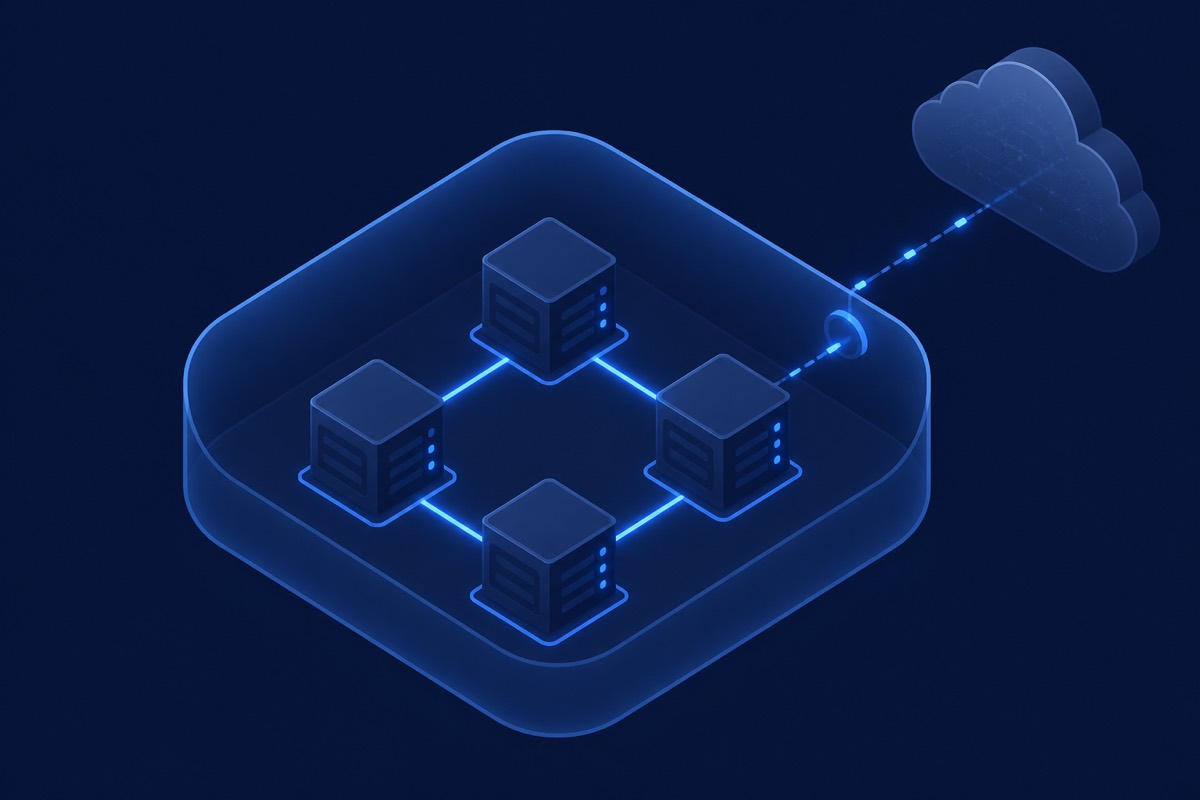
Virtual networks live under Network in the client portal, beside floating IPs and reverse DNS. An account can create 10 VNets by default. Contact support if you need more. Each VNet is an RFC1918 prefix between /29 and /24. MTU is 1450.
1. Open Network and create a VNet
Sign in, open Network → Private networks, and create a network. Give it a name you will recognize later. Enter a CIDR you do not already use on this account, for example 10.10.0.0/24. Do not use the network or broadcast address as a host IP later.
2. Optional gateway reference
The gateway field is optional and records your router's LAN address for reference. Configure guest routes yourself or through your DHCP server; saving this field does not change them.
3. Choose static addresses or your own DHCP server
LayerOne connects network interfaces without assigning private IPs or writing them into Cloud-Init. Configure static addresses inside your guests, or run DHCP on a router such as pfSense or OPNsense. LayerOne does not provide DHCP.
4. Attach servers
From the VNet, attach an existing VM, or select the network at deployment. No private IP is required. A server can join multiple networks, with one interface for each. The platform does not route between them.
5. Configure the guest interface
Bring up the interface and configure static addressing or DHCP in the guest. Some operating systems require a reboot to detect a newly attached interface. Existing guest addresses are not changed by saving the network's CIDR or gateway reference.
6. Optional: deploy without a public IP
Turn public IPv4 off during deployment when the server should stay isolated. You can still reach it from the browser console or from another server connected to the same private network. Public IPv4 cannot be added or removed after deployment, so keep it enabled if you are unsure whether the server will need direct internet access.
Know the current limits
- No LayerOne-provided NAT or internet gateway
- No IPv6 on private or public interfaces
- No editable network-wide forwarding rules
- No routing between your private networks unless one of your servers provides it
Use each server's Firewall page for its inbound and outbound rules.
Related
- Why configure a virtual network
- Using pfSense with LayerOne
- Docs: create a private network
- Client API (
private_networkon create; no private IP required)
Keep exploring
All articles →-
How to Self-Host Dawarich on a VPS
Run a private location-history timeline with Docker, PostGIS, Redis, background workers, HTTPS, and an off-server backup plan.
Read article -
How to Self-Host MicroBin on a VPS
Host a small paste and file-sharing service behind your own domain, require authentication, and keep its data off the public container port.
Read article -
How to Self-Host Gatus on a VPS
Build a lightweight status page from a YAML file, check HTTP and TCP services, and send alerts without running a full monitoring stack.
Read article